

Why DeFi Wallets Need to Explain Transactions, Not Merely Sign Them
You are about to swap a stablecoin for a volatile token before breakfast. The interface shows an exchange rate, a network fee, and a large “Confirm” button. Yet the transaction may do far more than transfer one asset: it can approve a contract to spend your tokens, route the trade through several pools, wrap or unwrap an asset, and leave you holding a position whose risks are not visible in the final balance. In DeFi, the difficult part is often not clicking through a transaction. It is understanding what the click authorizes.
That distinction matters for anyone using decentralized exchanges, lending markets, liquid staking systems, bridges, or yield protocols from the United States and elsewhere. A wallet is not merely a digital keychain. It is the place where human intent is translated into a set of machine-executed instructions. The strongest wallet experience therefore should not only protect private keys; it should help users inspect contract interaction, anticipate outcomes, and reconcile activity with the portfolio they think they own.
The hidden structure of a simple DeFi action
Consider a token swap. At the surface level, the user wants to exchange asset A for asset B. On-chain, the action may involve an approval transaction followed by a swap transaction. The approval gives a spender contract permission to move a specified amount of asset A. The swap then calls a decentralized exchange router, which may call one or more liquidity pools. If the transaction uses a permit mechanism, an off-chain signature may authorize spending without a separate on-chain approval, but that signature is still economically important.
This is the first useful mental model: a transaction is not the same thing as a user intention. It is an executable proposal that attempts to implement that intention under particular conditions. Gas settings, slippage limits, deadlines, token addresses, router contracts, and recipient addresses all shape the result. A wallet that displays only “swap token A for token B” hides much of the causal chain. A wallet that surfaces the chain of calls gives the user a chance to detect a mismatch before the transaction becomes irreversible.
Transaction simulation is valuable because it can estimate the resulting state before broadcast. In practical terms, a simulation may show expected balance changes, assets received, approvals granted, or warnings associated with a contract call. This is more informative than relying on a website’s button label, because the simulation examines the transaction payload that the wallet is actually being asked to sign. That does not make the result infallible. Simulation depends on the selected network state, the quality of the decoding, and assumptions about what happens between simulation and mining.
The limitation is important. A favorable simulation is not a guarantee that a protocol is safe. A contract can behave differently when market conditions change, when a block includes another transaction first, or when an external dependency returns an unexpected value. Simulations also cannot turn an unaudited or malicious contract into a trustworthy one. They are best understood as a pre-flight inspection: powerful for catching mismatches and obvious hazards, but not a substitute for protocol research or sensible exposure limits.
Approvals are permissions, not payments
Many wallet users treat an approval as a routine preliminary step. Mechanically, it is closer to issuing a spending authorization. Under common token standards, an allowance records how much a designated spender may transfer from the owner’s balance. If the allowance is unlimited, the contract may retain broad permission until the user changes or revokes it. That can be convenient for repeated interactions, but convenience expands the consequences of a compromised or deceptive spender.
This creates a trade-off rather than a universally correct setting. Limited approvals reduce potential loss if a spender later becomes dangerous, but they can require additional transactions and fees. Unlimited approvals reduce friction, especially for active traders, but they enlarge the authorization surface. The right decision depends on the protocol, the wallet’s operational habits, and the value at risk. What should not be accepted is treating every approval prompt as meaningless boilerplate.
A useful review habit is to ask three questions before signing: which contract is receiving permission, which token can it move, and how much can it move? The answer should match the action you intended. If a purported single-token swap requests permission over an unrelated asset, or if the spender address does not correspond to the protocol route you selected, stop and investigate. This simple comparison often provides more protection than memorizing a long list of generic security slogans.
Portfolio tracking is an accounting problem with a security edge
Portfolio tracking is commonly presented as a matter of adding wallet balances. DeFi makes that approach unreliable. A user may hold a receipt token representing a deposit, a liquidity-provider position whose value changes with pool composition, a debt obligation in a lending market, or a staked derivative that accrues value through an exchange rate. The visible token balance may be accurate while the economic interpretation is wrong.
For that reason, a useful portfolio view should distinguish assets from claims and obligations. A supplied asset is not the same as idle cash. A liquidity-pool token is not simply two underlying tokens sitting in a wallet. A leveraged lending position has both collateral and debt, and its risk depends on prices, liquidation thresholds, interest rates, and the behavior of the protocol. The non-obvious point is that portfolio tracking is partly a classification task: the system must infer what each on-chain position represents before it can summarize risk meaningfully.
Wallet-level tracking also has boundaries. Activity spread across several addresses, hardware wallets, custodians, centralized exchanges, and different networks will not automatically form one coherent balance sheet. Token prices can be unavailable, stale, or misleading for thin markets. Some positions are difficult to value because they depend on internal accounting rather than a freely traded token. A clean dashboard can therefore create false confidence if it presents an estimated dollar total without showing the assumptions beneath it.
For US-based users, this accounting perspective has a practical consequence beyond security: transaction records and tax reporting may require context that a simple balance history does not provide. The wallet can help organize evidence, but it does not decide the legal characterization of every swap, reward, bridge, or debt event. Users should preserve transaction details and obtain professional advice when the consequences are material. Software can improve visibility; it cannot remove ambiguity from an evolving regulatory environment.
What an advanced wallet should make visible
An advanced Web3 wallet should reduce the distance between a contract’s technical request and the user’s economic decision. That means clear contract and token identification, readable function data, expected balance changes, approval warnings, chain context, and a distinction between an on-chain transaction and an off-chain signature. It should also make it difficult to confuse a protocol website’s branding with the identity of the contract that will execute the call.
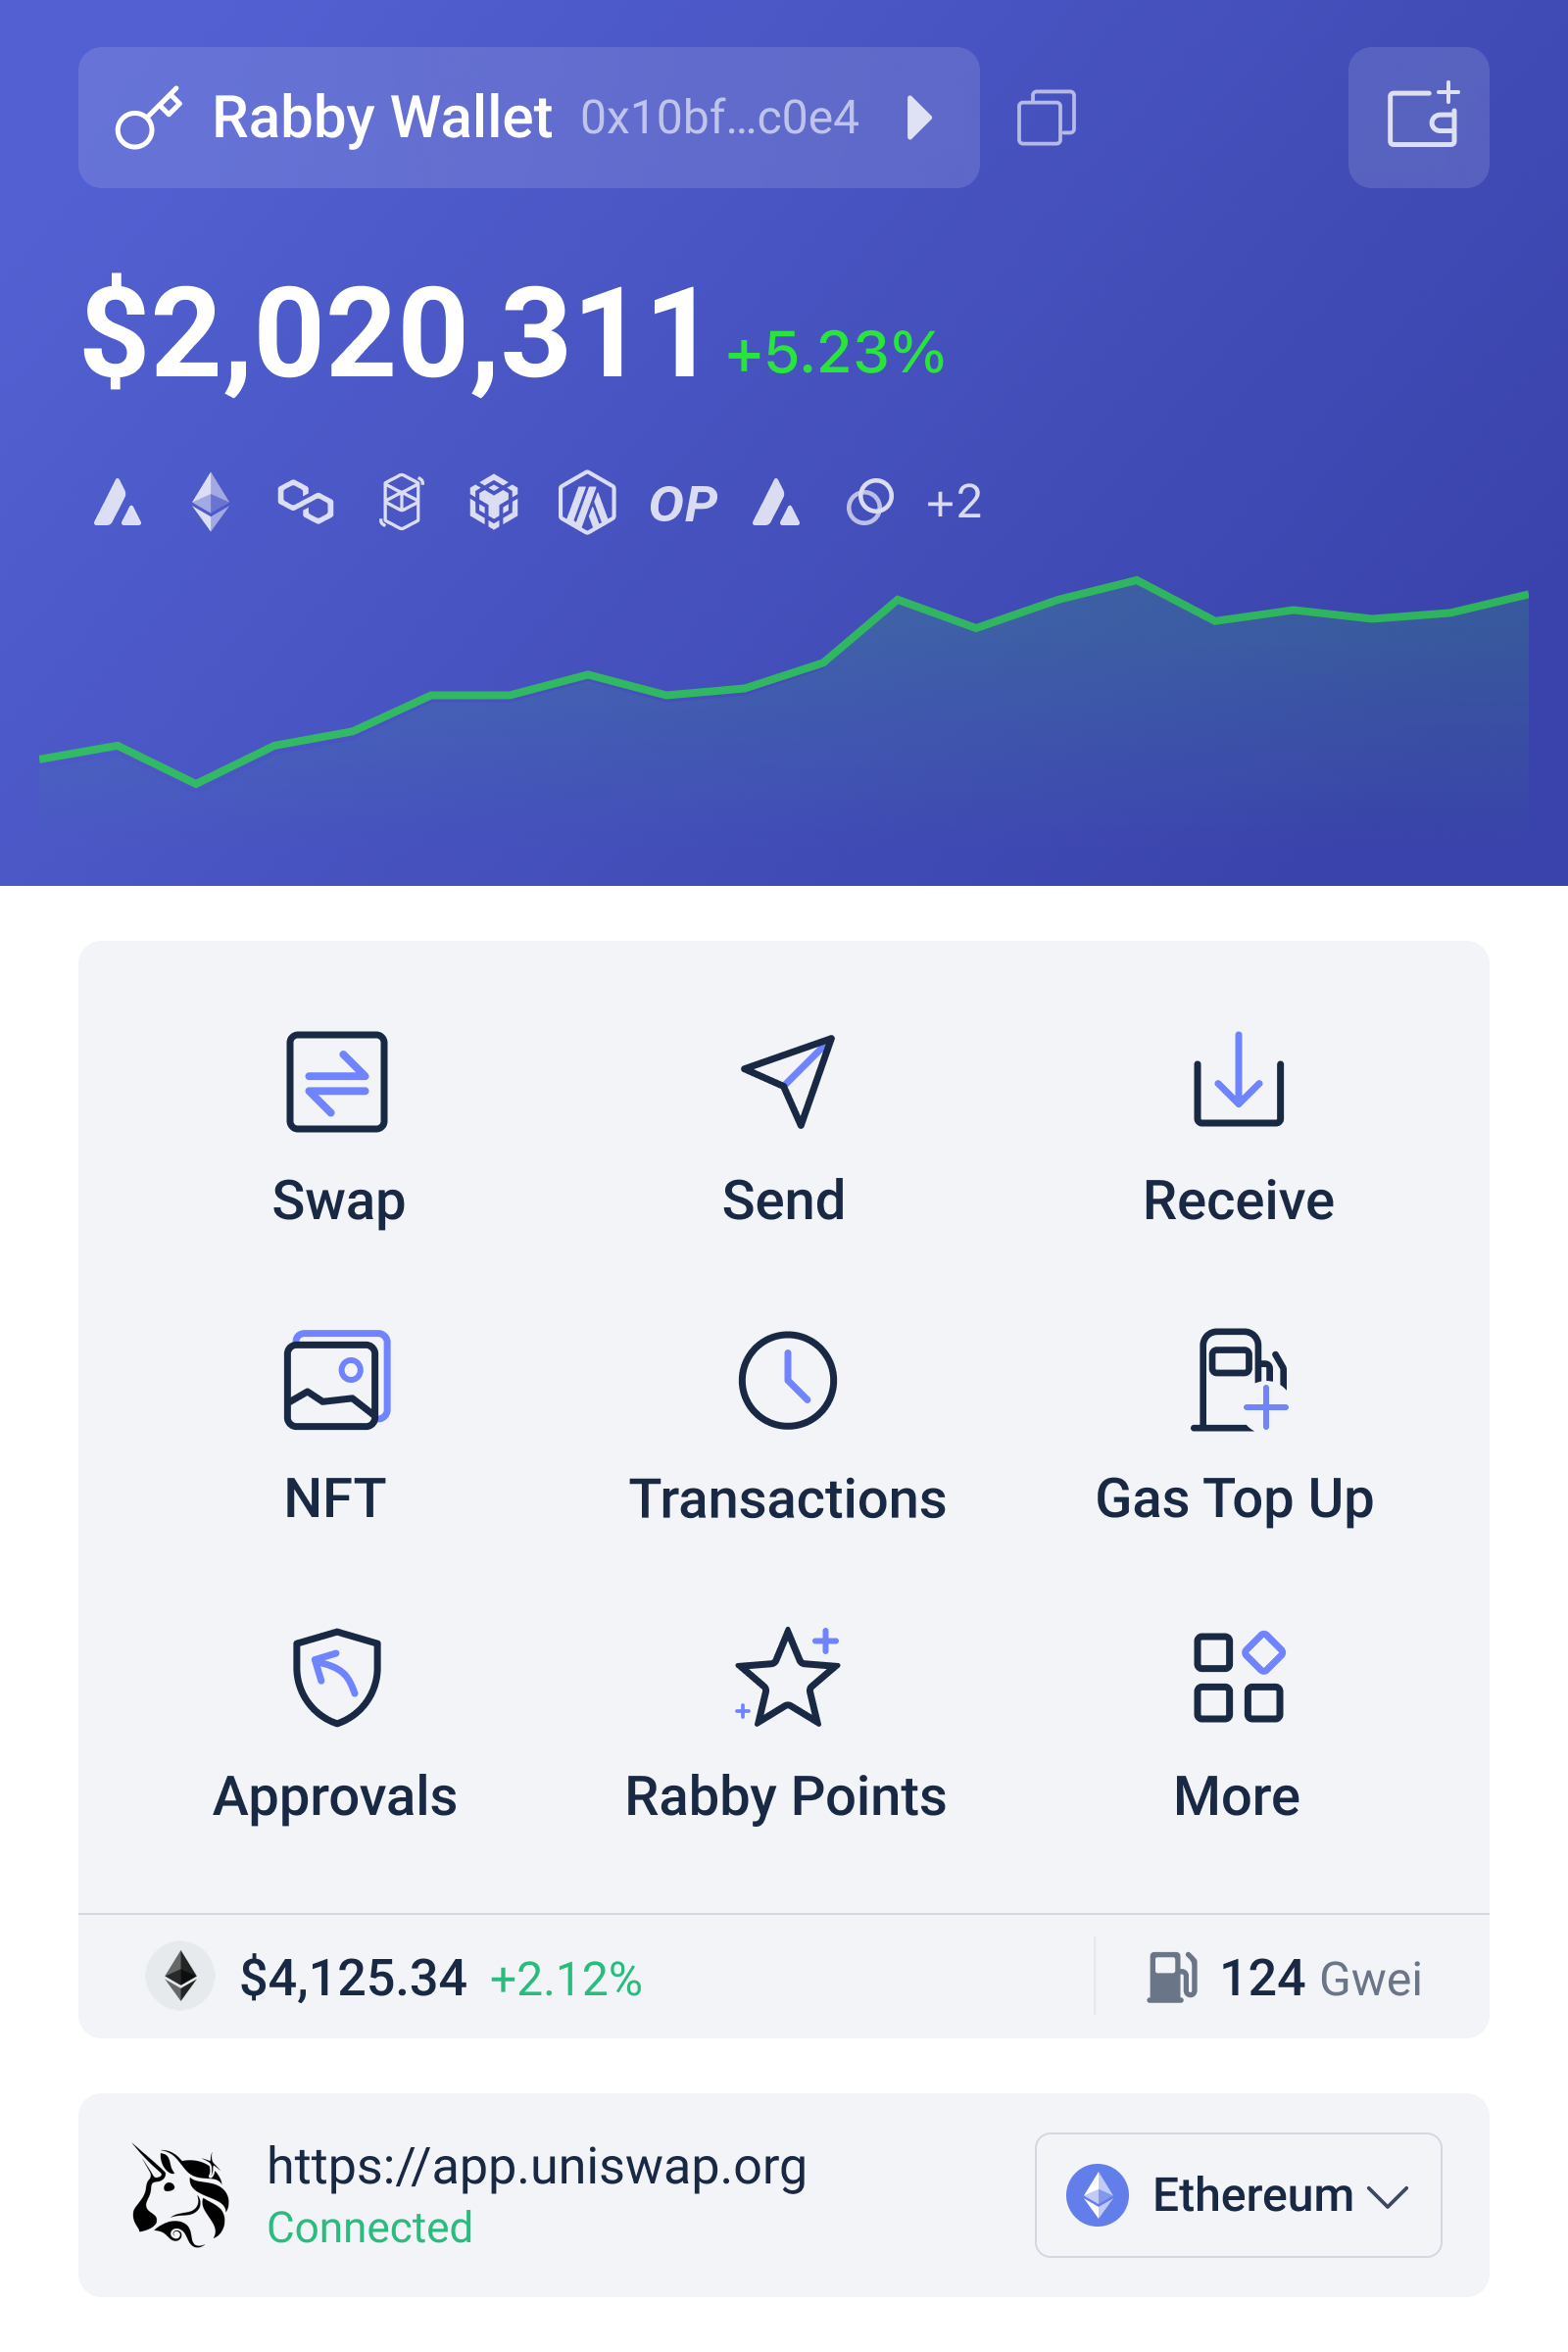
That is why tools focused on simulation and security can be useful to DeFi users exploring Ethereum and other EVM-compatible networks. Before connecting funds to a new application, readers can examine the wallet experience here. The value is not that a wallet can promise perfect safety. The value is that better inspection changes the decision from “this interface looks familiar” to “the requested state change is consistent with my intent.”
Still, warnings must be interpreted rather than blindly obeyed. A new contract may trigger caution because it lacks history, while an established contract may present fewer obvious warnings despite retaining meaningful economic risk. Conversely, a malicious application may use familiar-looking assets or social engineering to persuade the user to dismiss an alert. Security features work best as evidence in a broader process that includes checking domains, limiting approvals, separating long-term holdings from experimental funds, and reviewing transactions when the context changes.
A reusable workflow for safer interaction
Before signing, identify the intended outcome in plain language: “I want to deposit this amount into this lending market,” or “I want to exchange no more than this amount and receive at least that amount.” Then compare the wallet’s decoded request with that sentence. Review the network, recipient or spender, token amounts, minimum received, deadline, and any approval scope. If the transaction involves several calls, ask whether each one is necessary for the stated outcome.
After signing, verify the resulting state rather than assuming success from a green check mark. Confirm the expected balance change, receipt token, debt position, or allowance. When tracking a portfolio, record the role of the position: owned asset, deposited claim, borrowed liability, reward, or temporary routing balance. This makes future decisions easier because the portfolio becomes a map of economic exposures rather than a pile of token symbols.
Looking ahead, the most useful development would be wallets that combine transaction simulation with richer position-level explanations. If protocols expose more consistent metadata and wallets improve their decoding, users may be able to compare not only “what will change in my wallet” but also “how will my liquidity, leverage, counterparty, and smart-contract exposure change?” That outcome is conditional, not inevitable. It depends on standards, protocol cooperation, accurate pricing, and interfaces that communicate uncertainty instead of hiding it behind a single portfolio number.
Frequently asked questions
Can transaction simulation guarantee that a DeFi transaction is safe?
No. Simulation can reveal likely balance changes, contract calls, approvals, and certain inconsistencies before signing. It cannot prove that a protocol is honestly governed, that an oracle will remain accurate, or that market conditions will not change. Treat it as a strong inspection layer, not a complete security audit.
Why can my wallet balance differ from my actual DeFi exposure?
Because many DeFi positions are claims or obligations rather than ordinary token holdings. Lending deposits, liquidity positions, staking derivatives, and borrowed assets can have values and risks that are not obvious from a raw token list. Portfolio analysis must account for both assets and liabilities, including how each position is valued.
Should users always revoke unlimited token approvals?
Not necessarily. Revoking approvals can reduce the consequences of a compromised spender, but it may require additional transactions and fees. The sensible approach is to understand which contracts have permission, limit approvals when practical, and be especially cautious with unfamiliar or experimental protocols and high-value wallets.
The central lesson is simple but easy to lose in DeFi’s fast interfaces: signing is the final step of a reasoning process, not the beginning of one. A wallet becomes genuinely useful when it helps users connect technical instructions to economic consequences. Better simulation, clearer approvals, and more honest portfolio accounting cannot eliminate smart-contract risk. They can, however, make that risk visible early enough for a human being to make a better decision.

Bir cevap yazın